Your digital products run on open source software your team didn't write, and the EU CRA asks for diligence and attestation that it is secure. While AI helps your developers code faster, it pulls in open source packages without oversight. Starting September 11, 2026, the EU CRA requires you to report actively exploited vulnerabilities in your product, ahead of the full compliance deadline in December 2027. Non-compliance puts your EU market access at risk.
Talk to an expertOSS governance has always been an engineering problem, and the EU CRA just put a deadline on it that lands on your roadmap.
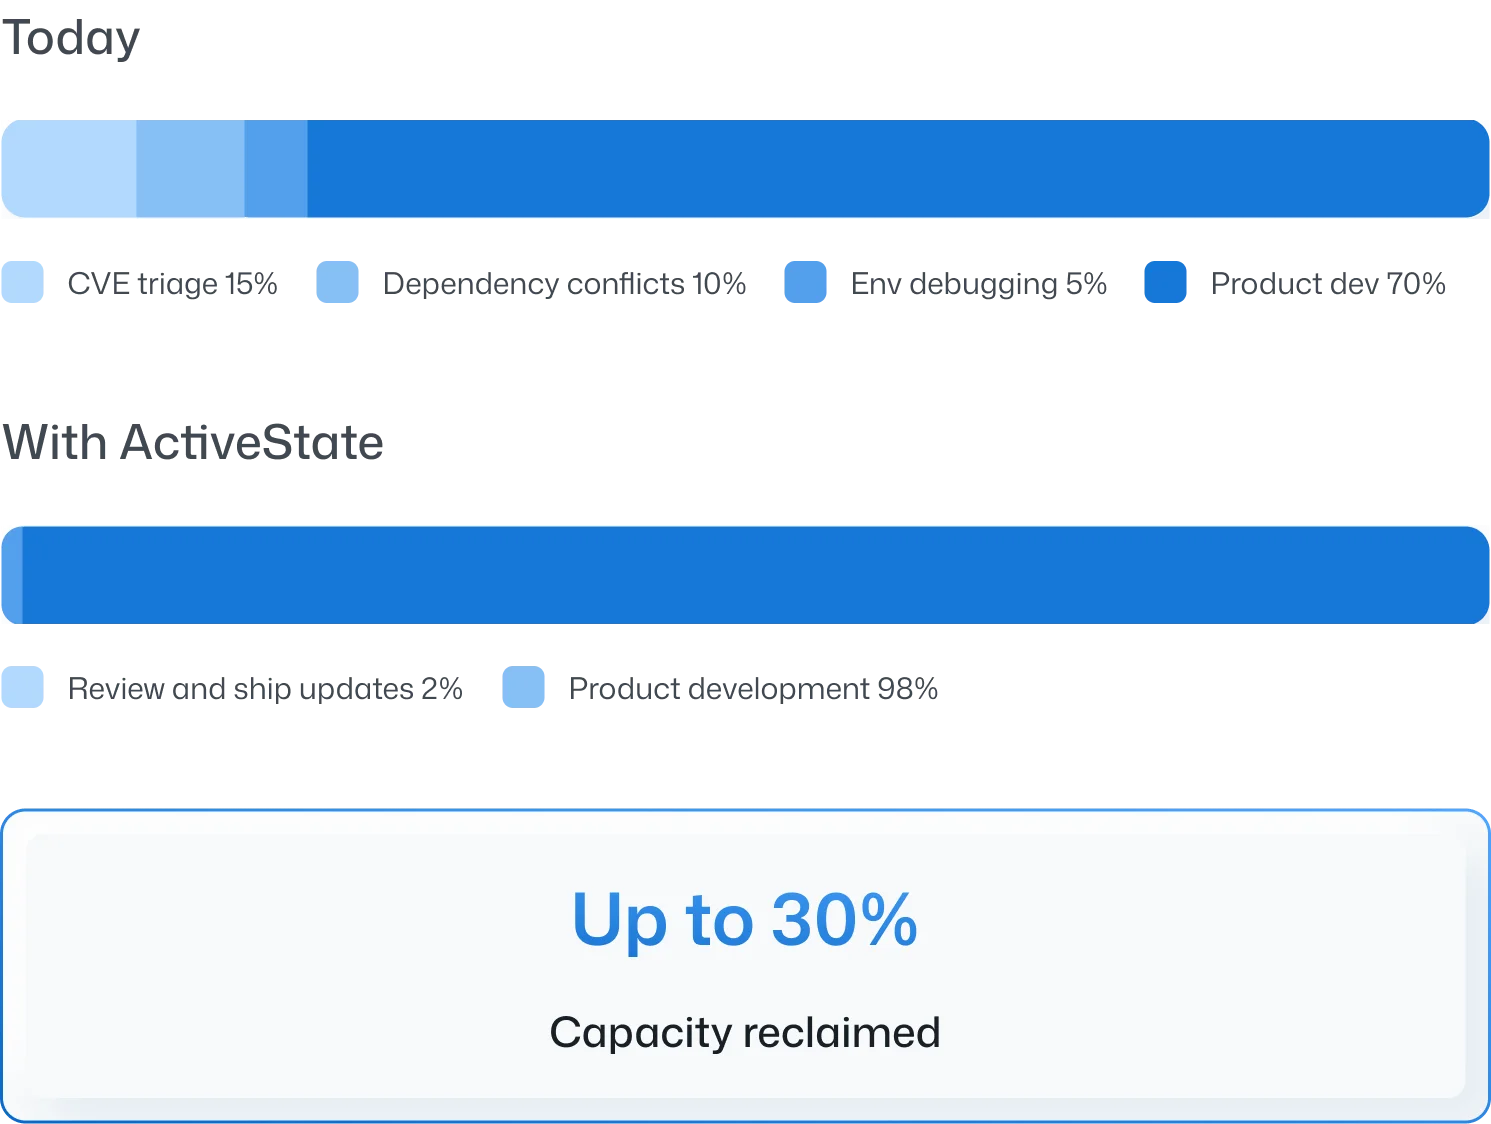
Security teams are handed a compliance obligation only possible to meet if their engineering teams prioritize things they’ve never been formally asked to do. Your organization will need a defined process that survives an audit, not a business practice that relies on individual memory.
Meeting the EU CRA's compliance demands is what protects your organization's EU market access.
of open source components in production are transitive, and your team didn't choose them directly.
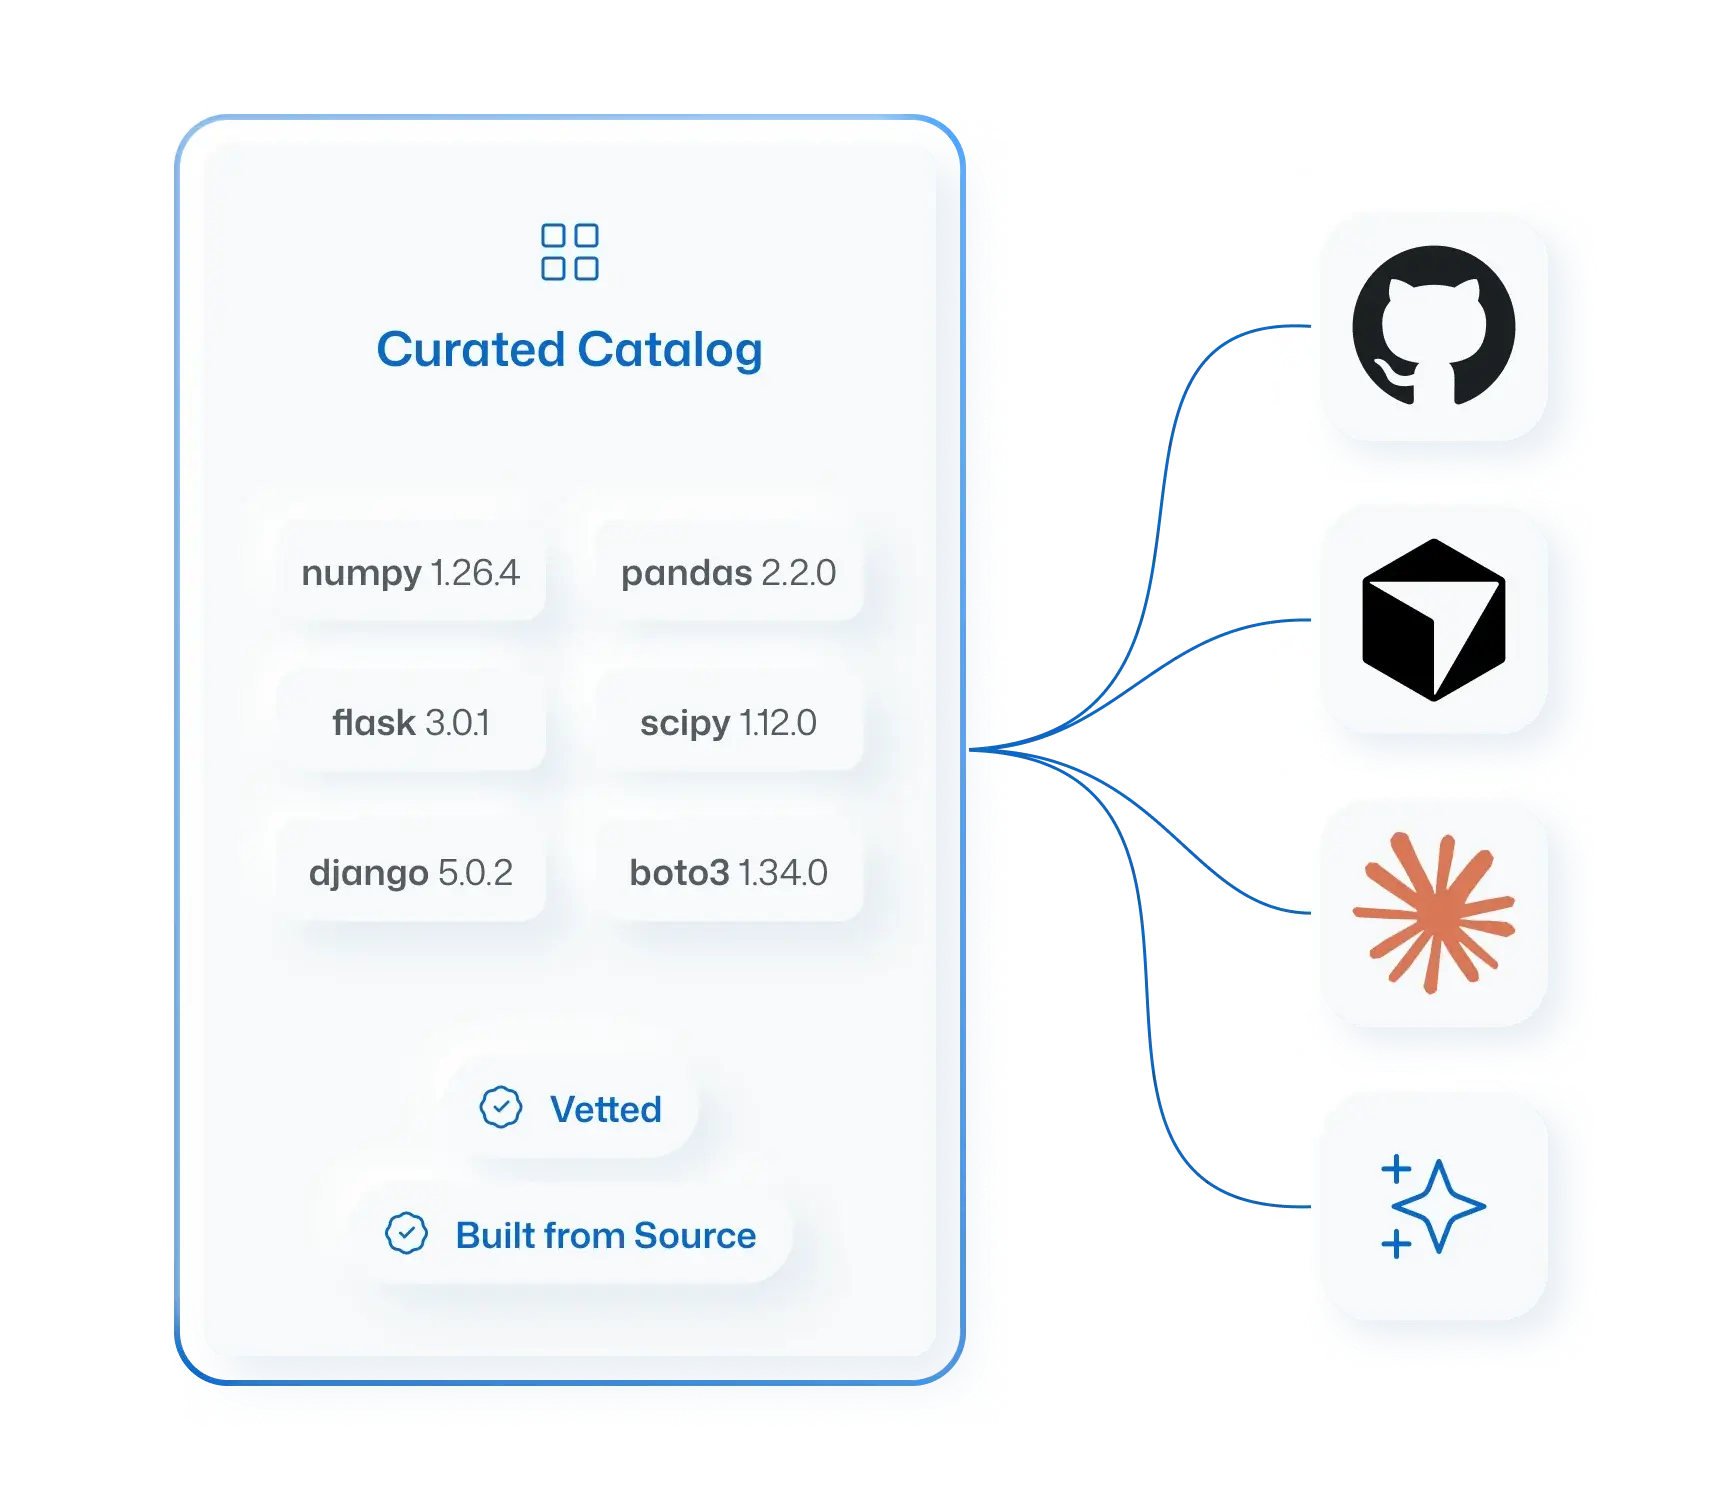
Source: Black Duck OSSRA 2025The ActiveState Curated Catalog aligns Security and Engineering on a single EU CRA compliance effort. It gives you a private, pre-vetted source of open source software, so fewer vulnerabilities ever reach your build in the first place. Security teams get full provenance and mitigated exposure. Engineering teams stop pausing sprints for security work.
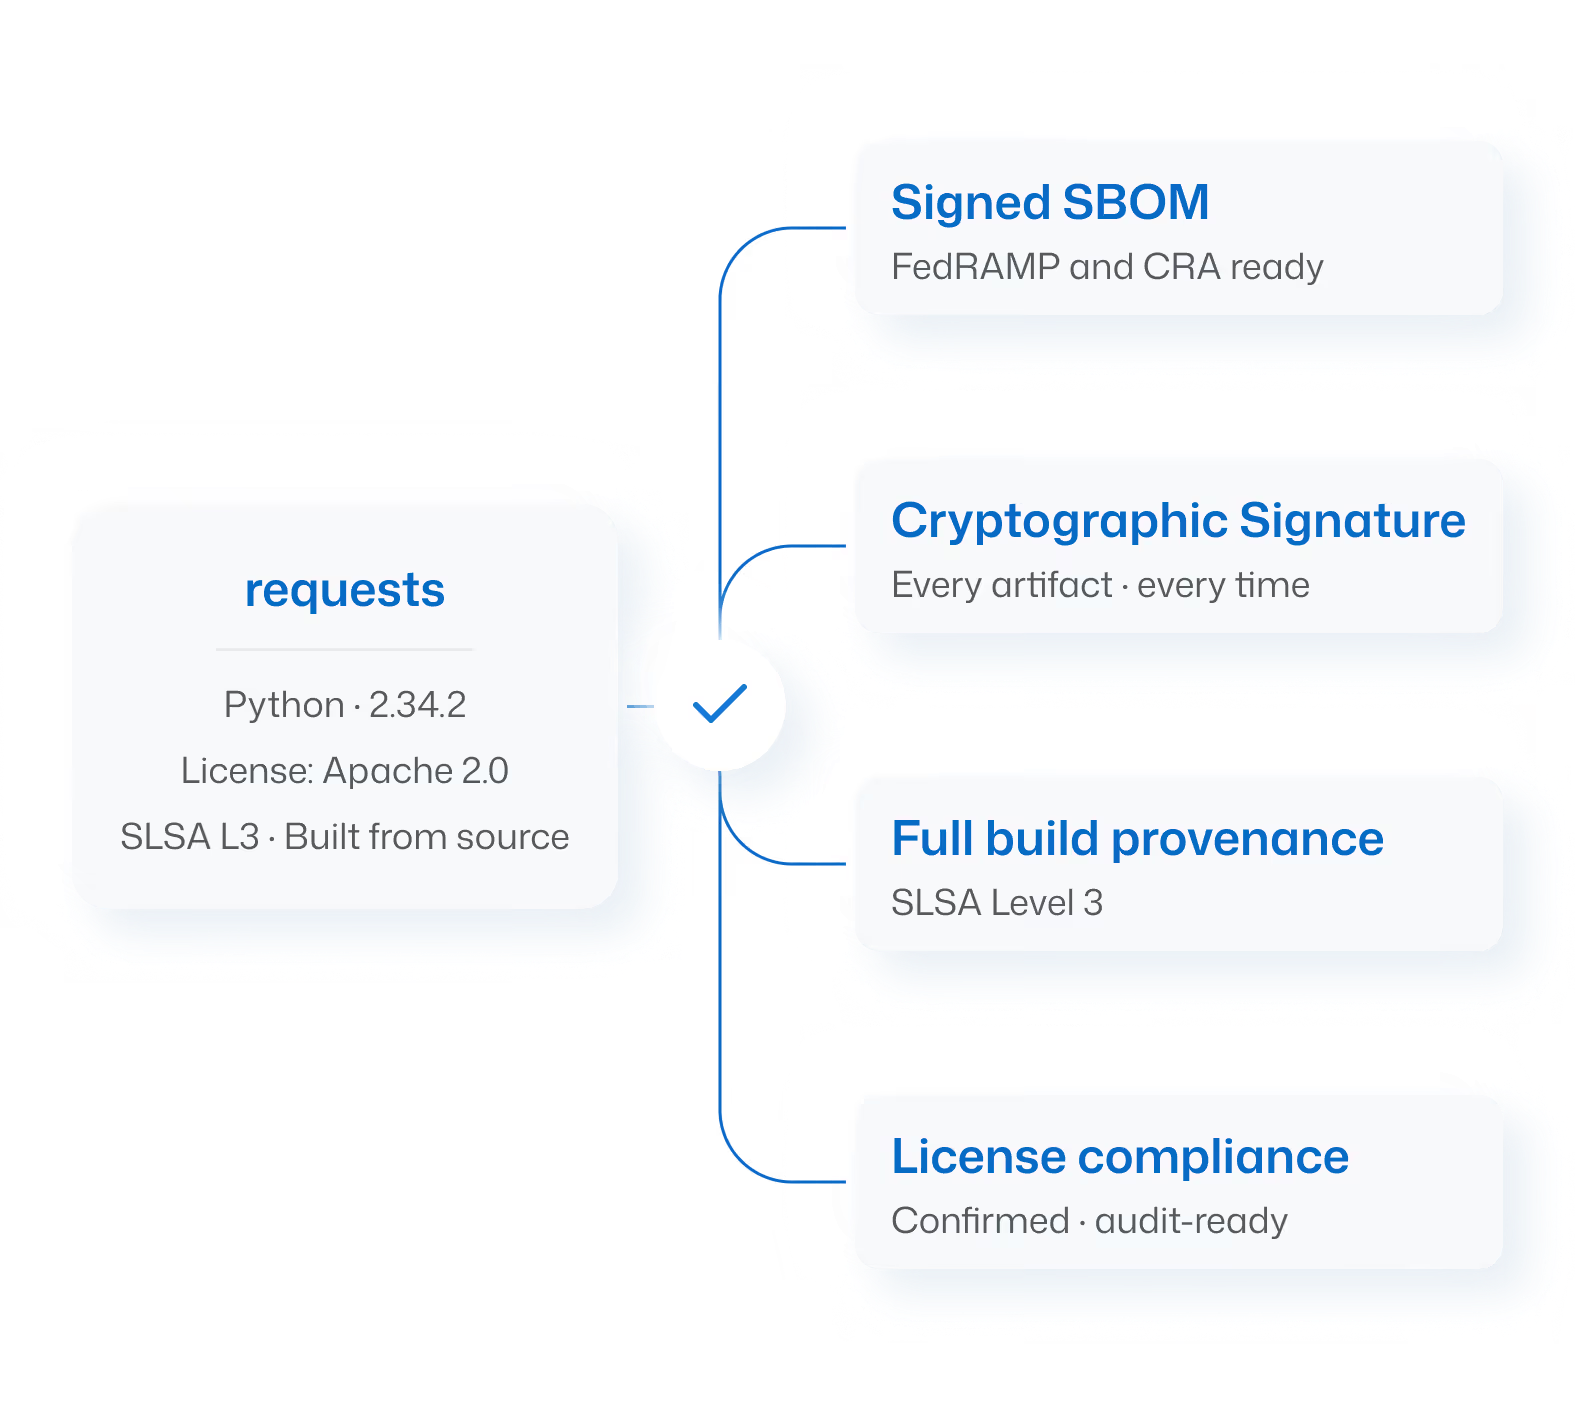
Automated, current SBOMs across every build
Cryptographic attestation and verifiable provenance, for every component
5-day Critical CVE remediation SLA
10 days for Highs, 30 for all others
A rebrand to "cyber resilience" means nothing without re-architecture.
Read more BlogPractical guidance on asset inventory, SBOMs, vulnerability prioritization, and container security.
Read more BlogThe container and SBOM angle.
Read more
